
Marsstein CompliancePlatform
GDPR gaps found, documents drafted, your sign-off.
Agents map your data flows, draft records of processing, DPIAs and policies from your own data, and list what is still open. Live for GDPR; ISO 27001 and the EU AI Act in preparation.
How it works
From your website to an approved record.
The agent reads what you already have, fills in what GDPR asks, drafts the documents and hands each one to you for approval.
01
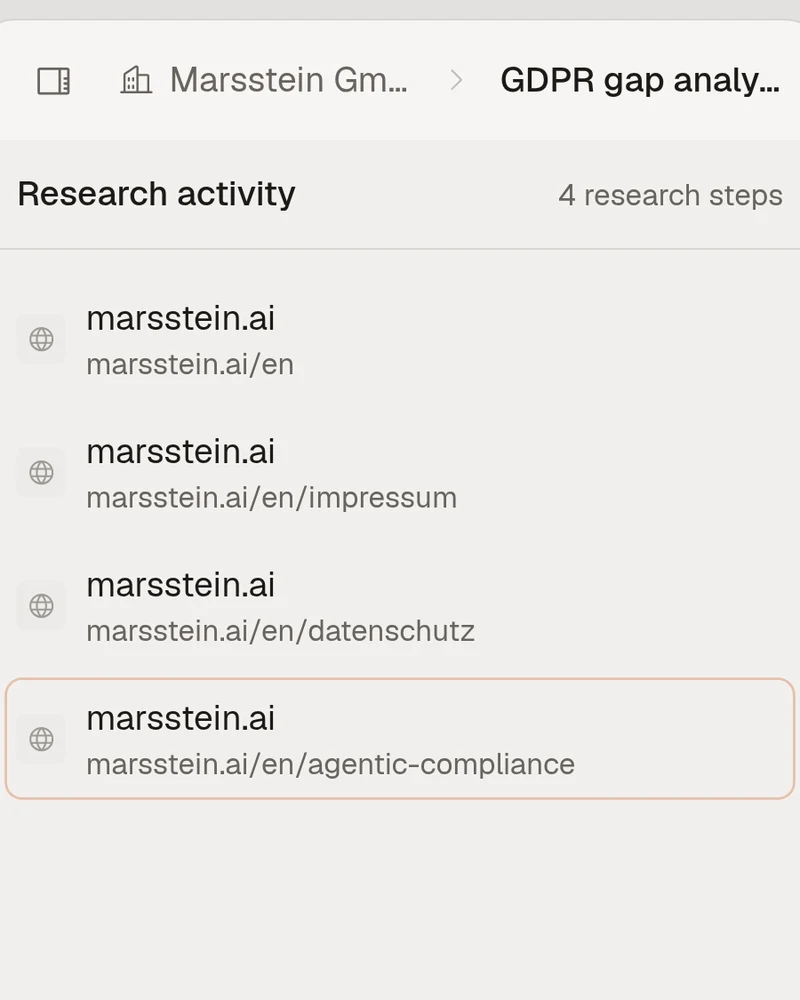
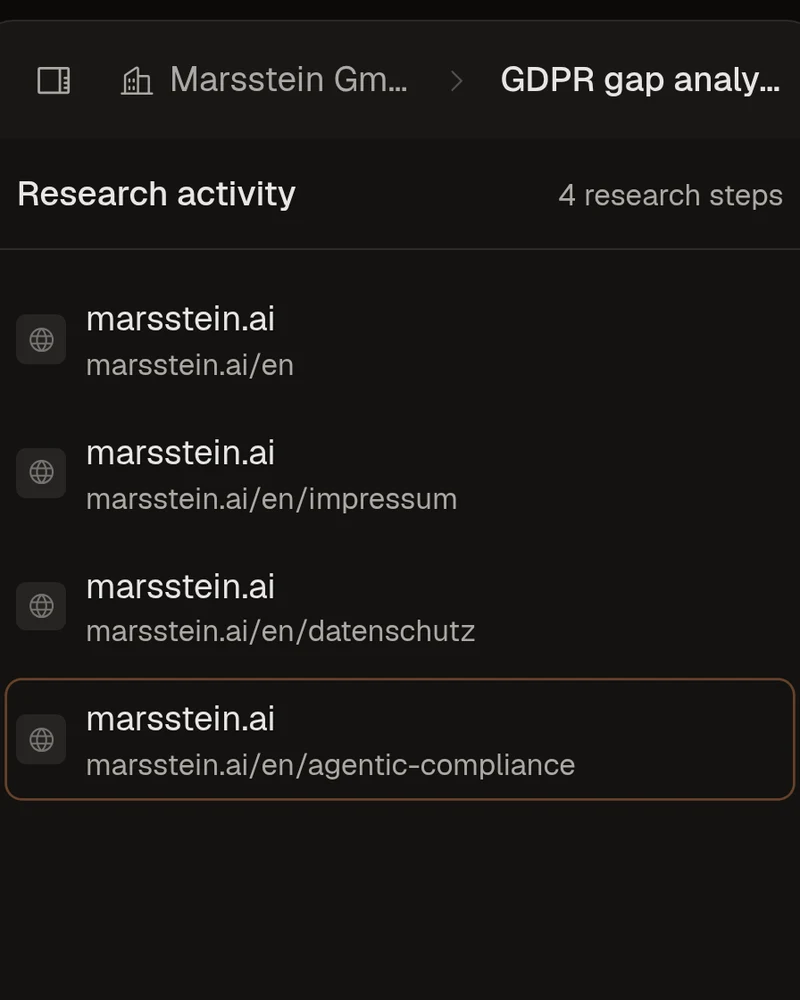
It researches
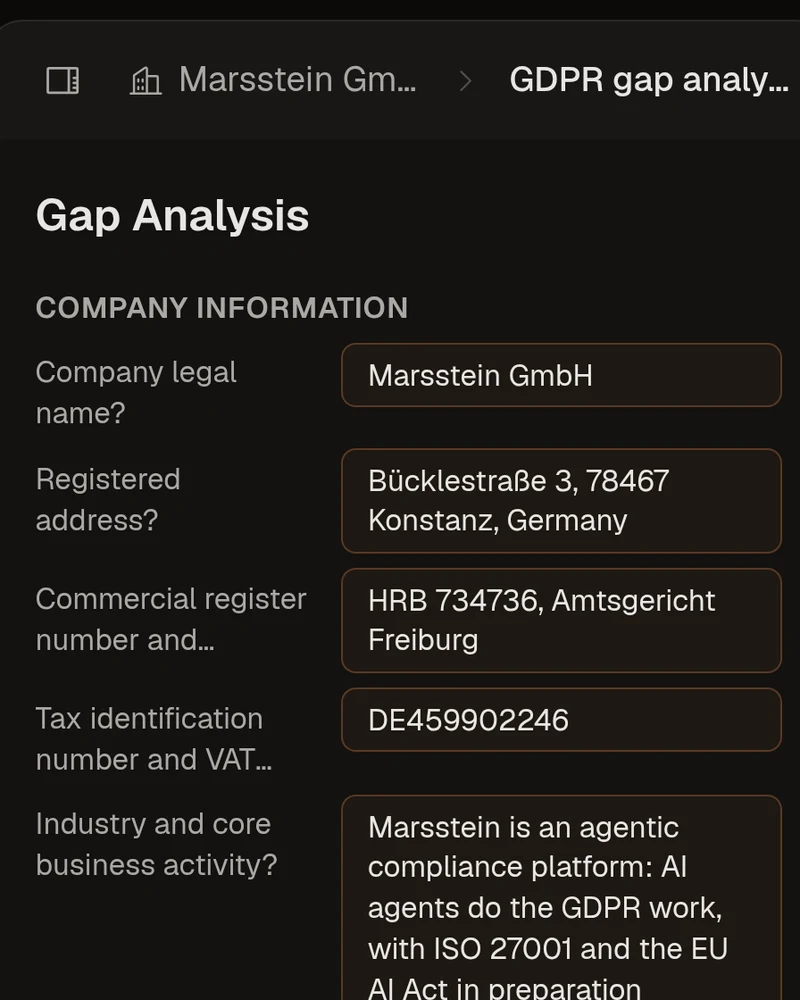
The agent reads your public website and the documents you upload, and lists every page it used.
02
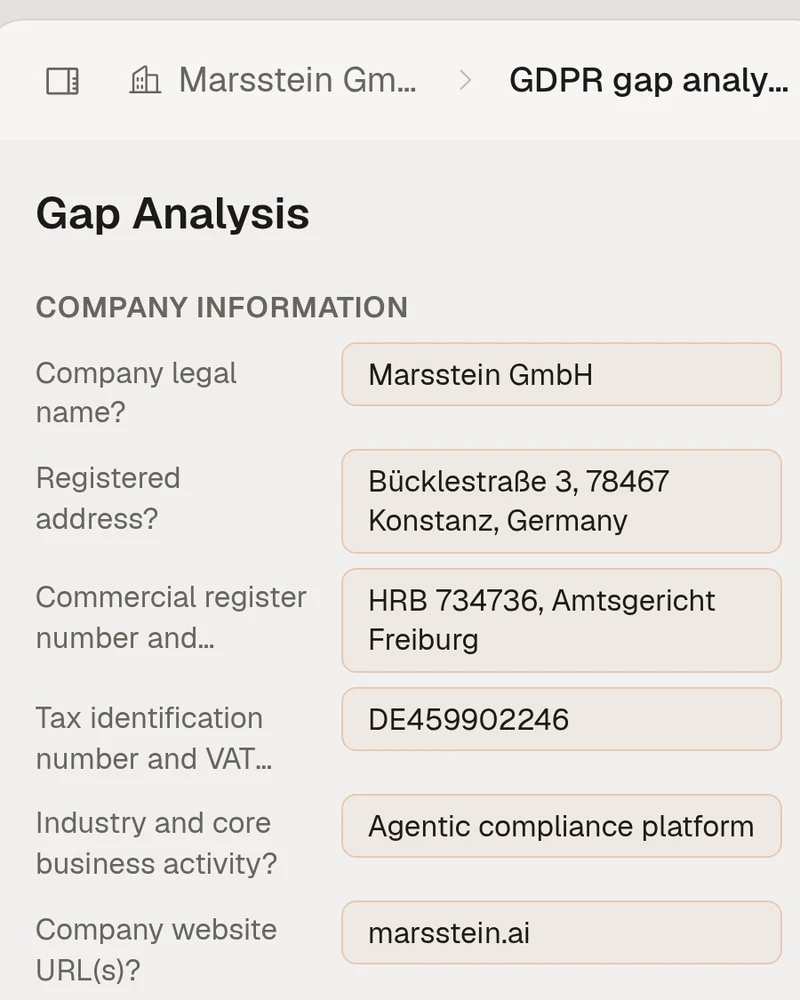
It prefills the gap analysis
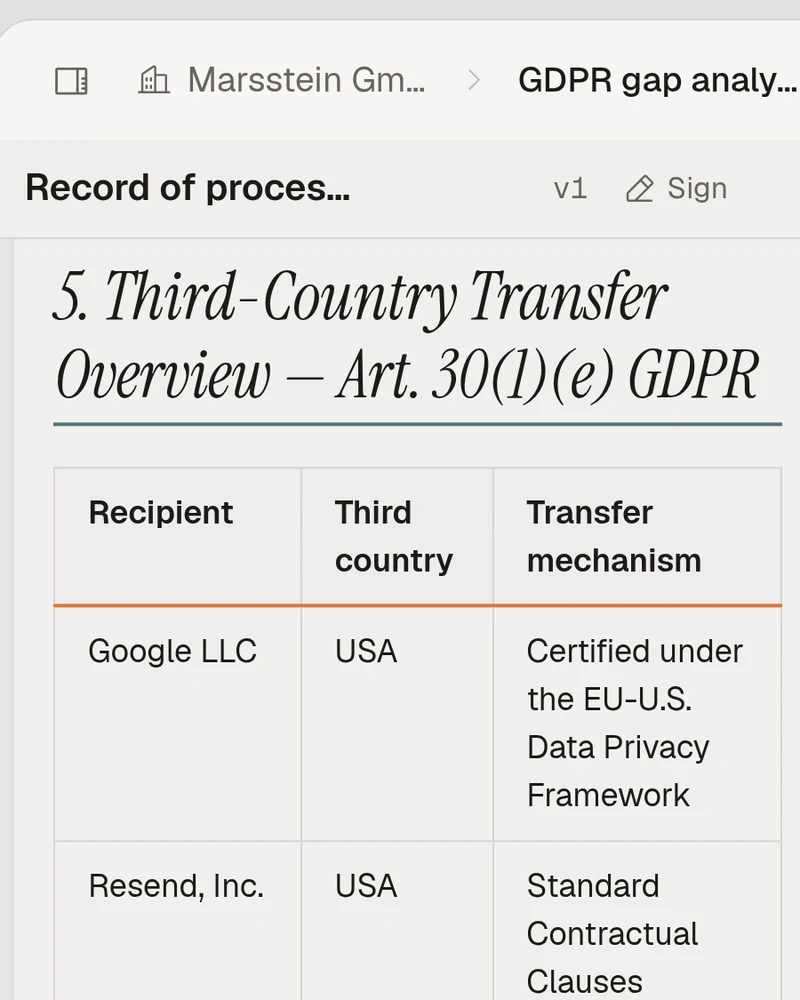
Company details, privacy policy, representatives and transfers are filled in from what it found. You check each answer.
03
It drafts the documents
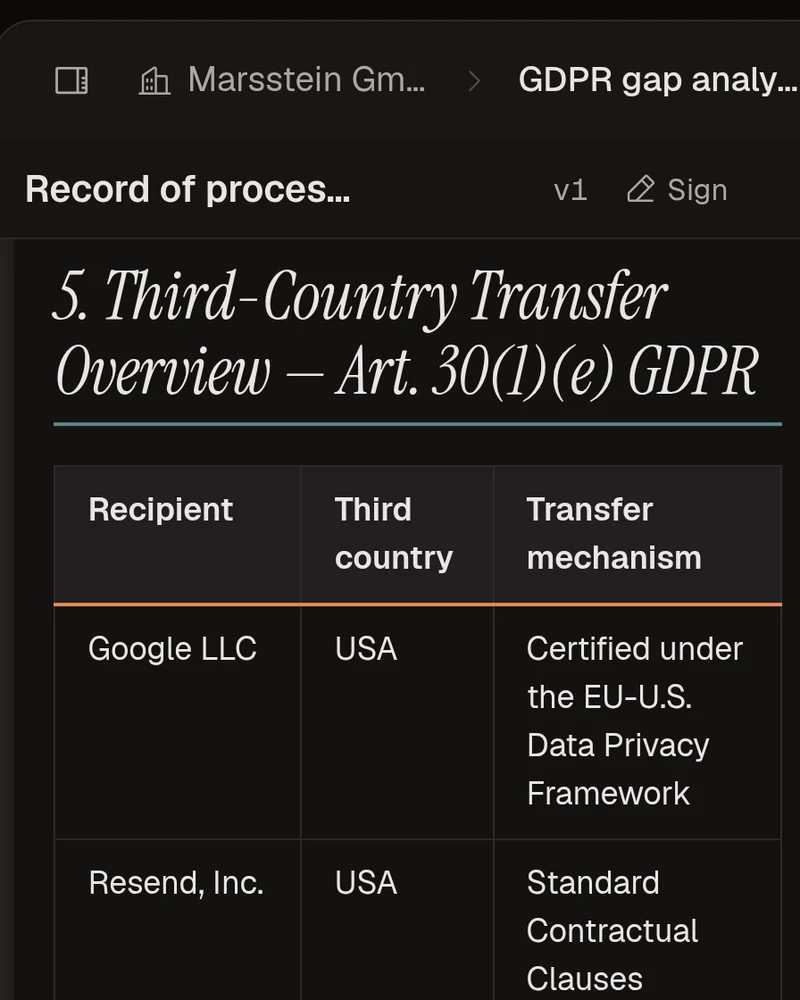
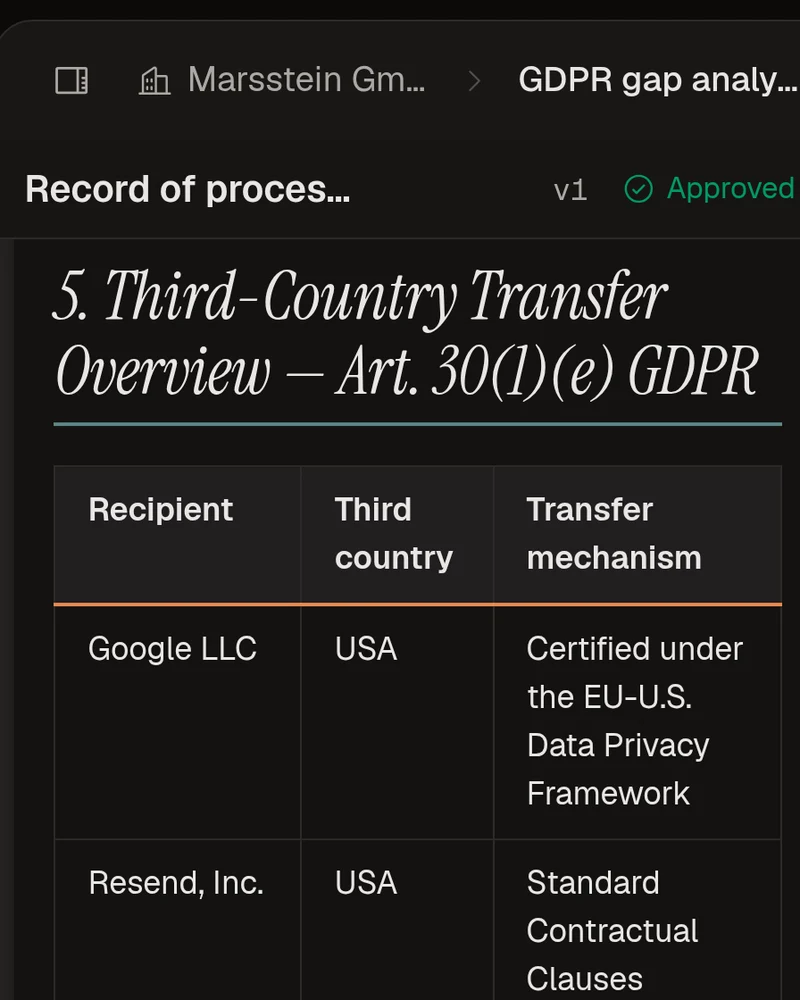
The record of processing activities is written section by section, from the controller's details to the technical and organisational measures.
04
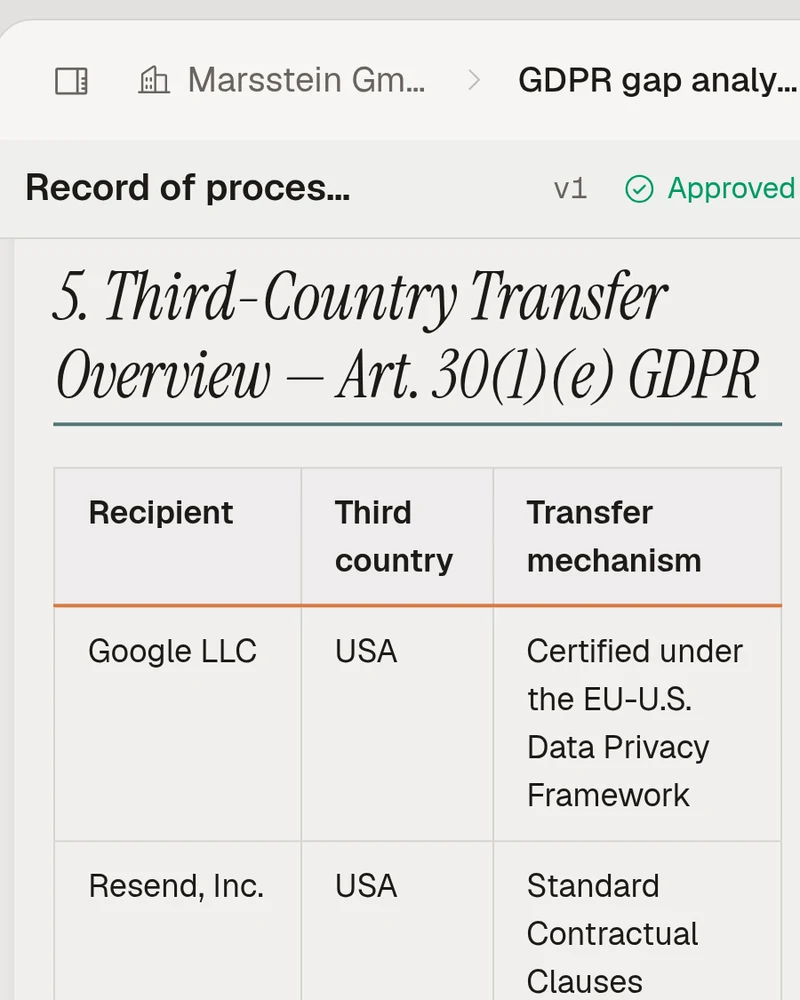
You approve
Nothing is final until a person on your team approves it. Approved documents stay in the library with their state.


What the agents draft
The documents GDPR asks for.
Each one starts as a draft from your own information and becomes final only with your approval.
- GDPRLive
- ISO 27001In preparation
- EU AI ActIn preparation
Records and assessments
- Record of processing activities (Art. 30)
- Data protection impact assessment (DPIA)
- Transfer impact assessment (TIA)
- Legitimate interest assessment (LIA)
- Fundamental rights impact assessment (FRIA, EU AI Act)
Contracts
- Data processing agreement (Art. 28)
- Joint controller agreement (Art. 26)
- Standard Contractual Clauses, all four modules
- Non-disclosure agreement
- Works council agreement
Notices and policies
- Privacy notice
- Cookie policy
- Technical and organisational measures (TOM)
- Data retention policy
- Data subject request procedure
- Consent form
Data breaches
- Notification to the supervisory authority
- Notification to affected people
- Breach register
- Breach response plan
Frequently asked questions
Your question is not listed? Ask us directly.
Talk to usWhat is agentic compliance?
AI agents that research your company, find the gaps against the regulation and draft the required documentation for your approval, rather than tools that only store what you type in.
How is it different from a GRC dashboard?
A GRC dashboard organizes what people enter. Here the agents find what needs doing and draft it; you review and approve.
Is the AI itself GDPR compliant?
We document our own processing the way we ask you to: our privacy policy names every service that processes personal data and the safeguard for each transfer outside the EU. The AI features use the Google Gemini API, and Google does not use data submitted through it to train its models.
How long does it take to get started?
Sign in, let the agent research your company and prefill the gap analysis, then review the first drafts with our team. How long that takes depends on your company; we agree the plan with you.